








Cryptojacking: when a machine mines for somebody else
How mining malware gets in, why a rig owner is both the best placed and the easiest to fool, and how to check and clean a machine properly.
What is cryptojacking?
Cryptojacking is someone running a miner on hardware they do not own or pay for. It is not rare. It is the most common thing malware does with a machine once it has one.
The reason is simple: the payout needs no victim to be tricked into anything afterwards. The electricity is the victim, and it bills quietly.
It is nearly always Monero. That coin can be mined at a profit on ordinary processors, so a few thousand office desktops are worth having. Its privacy also means the money cannot be followed.
The program is usually XMRig, an ordinary open-source miner. Only its name and configuration are changed.
A machine mining for someone else does not look infected the way people expect. Nothing is encrypted, no file is missing, no ransom appears. It just runs hot, throttles, wears out its fans, and costs money.
Why is it different when you already mine?
Generic articles all say the same thing: look for high processor use, heat and loud fans. On a rig, all three are normal. So the usual advice detects nothing.
Being a miner makes you the best-equipped person to find this. It also makes you the easiest to fool.
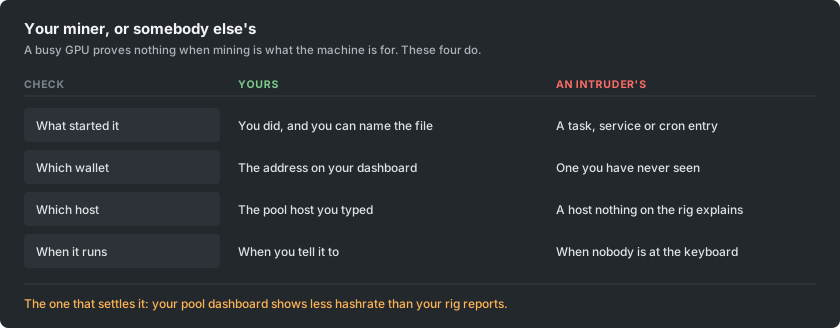
Your advantage is a second, independent record of what your hardware produced. Your pool dashboard is measured on someone else's server, from work that actually arrived.
Compare it with what the rig reports. First allow for stale shares, which are shares that arrived too late to count. If the dashboard is still well below the rig, something is consuming the difference.
How does a miner get onto a machine?
The routes have not changed much. None of them needs a sophisticated attacker.
- Cracked and pirated software. This is still the biggest single source. A keygen or patched installer is a program you agreed to run with your own permissions. The miner rides along inside the archive.
- Anything exposed to the internet without a patch. Old, widely known holes in server software are scanned for all the time. A miner is the favourite payload, because it earns money from a machine that holds nothing worth stealing.
- USB drives. Recent campaigns copy themselves onto removable drives. They hide behind a shortcut that looks like the drive icon. That is how a network with no internet exposure still gets infected.
- Container and build images. A base image pulled from a public registry can carry a miner. It then mines inside every environment built from it.
- A browser tab, though far less than before. Scripts that mine while a page is open were an industry until the largest provider shut down in 2019. They still exist on streaming and download sites, but they stop when the tab closes.
What are the signs on a machine that should be idle?
- It never really idles. Fans stay up and the case stays warm with nothing open.
- A process you cannot account for. It is often named to look like a real system process. A single character difference in a familiar name is a common trick.
- Use that drops the moment you open the task manager and returns when you close it. That behaviour is deliberate and is close to proof on its own.
- A scheduled task, service or startup entry nobody created.
- Outbound connections to a host you do not recognise, repeating on a fixed rhythm.
What are the signs on a rig that should be mining?
Here the question is not whether something is mining. It is whether everything that is mining is yours.
- The dashboard sits below what the rig reports, consistently, by more than stale shares explain.
- Two mining processes where you started one. On a multi-GPU rig, it is worth counting.
- Your start script or flight sheet holds a wallet address or host you did not type. Read it, do not glance at it. An address altered in the middle looks identical at a glance.
- A card runs hot but produces nothing on your pool. That is what a second miner pinned to one device looks like.
- It mines after you stopped it. If halting your own miner does not quiet the machine, something else is running.
What is the wallet swap, and why does it cost more?
A separate family of malware does something worse and simpler. It watches the clipboard. When you copy something shaped like a wallet address, it swaps in the attacker's address.

It picks an address that begins and ends with the same characters as yours. So a quick check passes. People have lost large sums this way with no mining involved. The two kinds of malware are often installed together.
Miners face a second version of the same idea. The address inside a start script or flight sheet is rewritten once. Every payout afterwards goes somewhere else.
Nothing breaks, and the rig mines perfectly. The money simply arrives at a different wallet. People usually discover it when they wonder why a payout never came.
The defence is dull, and it works:
- After pasting an address anywhere that matters, check the whole thing, not just the ends.
- Confirm the address on your dashboard is the one you meant.
- If your payouts stop while your hashrate does not, check the address before anything else.
How do you check a machine, step by step?
Work through these in order:
- Compare the two hashrates. Put what the rig reports against the pool dashboard, over a day rather than a minute.
- Read your own configuration. Check every wallet address and every host, character by character, on every rig.
- Stop your miner and watch. A machine that stays busy afterwards has something else running.
- List what starts by itself. On Windows, check scheduled tasks and services. On Linux, check timers and cron. Check whatever runs at login too.
- Look at outbound connections while your own miner is stopped. Anything still talking on a rhythm is worth naming.
- Scan with something reputable, but do not stop at a clean result. Miners are often modified until scanners no longer recognise them. That is why this step is last, not first.
Why is deleting the file not enough?
These miners are built to come back. Deleting the program while whatever starts it survives buys a few minutes.
Remove things in this order:
- The scheduled task, the service, the startup entry, the cron line and the registry key.
- Then the file itself.
- Then reboot, and check that nothing has returned.
Consider a rebuild on a machine that mattered. That goes double for anything that has held a wallet or a private key. The same access that installed a miner could install anything else.
A modern campaign will also have collected passwords on the way through. Change the passwords that machine has seen, from another device.
How do you stay clean?
The rules that prevent this are boring. People skip them because mining means downloading unsigned software from strangers.
- Get miners from the project's own release page, and check the published checksum. A miner from a forum link, video description or repacked archive is the most likely way a rig gets infected. You expected a warning, so you dismissed it.
- Never run cracked software on a machine that mines or holds a wallet. Ever. The two habits do not mix.
- Patch anything exposed to the internet. Most infections are automated and pick machines by version number.
- Keep the wallet you are paid to separate from the machine that mines. A rig only needs an address, never keys.
- Check your payout address after any change to a rig. Check it again after anything unexpected happens to it.